Is your board treating philanthropy as a relationship or a transaction?
Posted on 17 Sep 2026
Charities reported $14.8 billion in donations and bequests last financial year, the second-highest…
Posted on 15 Oct 2026
By 'Governance Guru' Nina Laitala, training lead, Community Directors
A few years ago, I sat on a small community board that was still held together by email threads and printouts.
There was no central place to store documents, there was no version control, and meetings were regularly derailed by directors working from the wrong file or an out-of-date quote. As a subcommittee member, before I joined the board, I pushed hard for cloud-based storage. The outgoing chair and manager set this up as one of their final tasks together, and when I formally joined the board, everyone assumed I would take ownership of it, because I had suggested it in the first place.
Almost immediately, I discovered the platform was not fit for purpose. It was too complicated for most directors to use, and it was expensive. The organisation had spent its money on a tool that solved nothing.
That experience still shapes how I think about digital inclusion. It is tempting to treat digital inclusion as a question of access alone: can everyone use our website, our forms, our portals? But digital inclusion and cyber security are two sides of the same governance coin. If we choose a tool that nobody can use safely, or that exposes client and donor data because it was chosen without expertise or understanding, it is not inclusive. It is a threat.
Boards sometimes assume cyber security sits with whoever is "good with computers". Sometimes this is staff, a keen volunteer, or a director who happens to work or have experience in tech. That is effectively what happened on my board. Ownership fell to me not because I had the right skills, but because I had raised the idea first.
Cyber risk deserves the same governance attention boards give to financial risk. Infoxchange’s most recent annual Digital Technology in the Not-for-Profit Sector Report (2025) found that fewer than half of not-for-profits with 150 staff or fewer have effective processes in place to manage information security risks, and only one in five regularly run cyber security awareness training for staff and volunteers.
Whether your board has three volunteer directors or 30 staff supporting it, the responsibility does not change but the capacity does. Where a small board might lean on a trusted external adviser or advice from sector colleagues, a larger organisation might have a dedicated IT manager. Either way, the board sets direction, sets risk appetite, and asks the hard questions. It does not outsource its duty of oversight along with the task: the ownership stays with the board.
"A standing cyber item on the board agenda, even a brief one, keeps the question live rather than buried until something goes wrong."
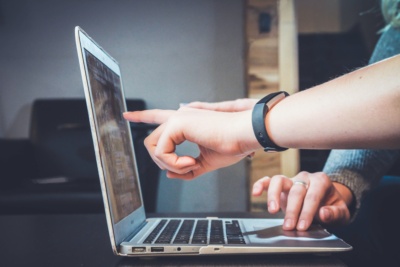
Before adopting any digital product, ask who it needs to work for. Not just staff, but members, volunteers, and the clients or service users the organisation exists to support. My board's cloud storage failed this test twice over: it was too complex for most directors, and nobody had checked whether it protected the sensitive information stored inside it.
Fit for purpose and secure are not separate questions. A platform that is hard to use invites workarounds such as staff using personal devices, sharing passwords, and emailing screenshots around. That is exactly the kind of human error most cyber incidents rely on.
Cheap tools can be costly if they create risk, and expensive tools can be wasteful if nobody uses them properly. Boards should weigh the ongoing cost of licences, support and training against the cost of a breach, in terms of dollars and reputation.
Decide upfront how you will know when a tool has become obsolete or unsafe. Do you know who has access to what? Is there a process for rescinding that access when people leave the organisation? Do you know when your last security review or audit happened? A standing cyber item on the board agenda, even a brief one, keeps the question live rather than buried until something goes wrong.
Finally, be honest about blind spots. Boards made up of people who are comfortable with technology can easily miss the barriers facing members, clients or colleagues who are not. Barriers might include age, access to devices and stable internet, language, and time. Ask who isn't using the tool, and why.
Digital inclusion doesn’t just mean opening the door wider. It means making sure that what's behind the door is safe for everyone who walks through it. That is a governance job and it belongs squarely with the board.
If you want a starting point, the ICDA cyber security self-assessment tool for community organisations is a practical way to see where your board's oversight stands today and when it's time to check again.
Community Directors hosts thousands of pages of free guidance, such as this help with your tech: Damned Good Advice on Cybersafety and Fraud Prevention | 10 questions every board member needs to ask about cybersecurity | Preparing a technology plan for your organisation | Cybersecurity policy | Data retention and destruction policy | More help with tech | More help with artificial intelligence
Find more resources under tools and resources on the Community Directors website.
Posted on 17 Sep 2026
Charities reported $14.8 billion in donations and bequests last financial year, the second-highest…
Posted on 13 Aug 2026
Innovation isn't just a buzzword, and it isn't just about technology. It’s a necessary part of…
Posted on 22 Jul 2026
I once worked with an organisation that had become expert at keeping the lights on. Every year it…
Posted on 10 Jun 2026
ICDA training lead Nina Laitala examines the governance issues facing Australian not-for-profits.
Posted on 18 May 2026
ICDA training lead Nina Laitala examines the governance issues facing Australian not-for-profits.
Posted on 12 Mar 2026
Fundraising is often parked in the operational corner. And yes, the execution of fundraising is an…
Posted on 10 Dec 2025
Stressed, overwhelmed, exhausted… if you’re on a not-for-profit board and these words sound…
Posted on 11 Nov 2025
I’ve seen what happens when fear of conflict wins out over taking a principled stand.
Posted on 15 Oct 2025
Writing grant applications is usually seen as an operational job, but that doesn’t mean the board…
Posted on 18 Sep 2025
Organisations using artificial intelligence to transcribe and summarise meetings must ensure they…
Posted on 14 Aug 2025
ICDA training lead Nina Laitala examines the governance issues facing Australian not-for-profits.
Posted on 17 Jul 2025
ICDA training lead Nina Laitala examines the governance issues facing Australian not-for-profits.